Pages

Monday, October 3, 2011

Vulnerable Facebook Applications

Facebook has always been under the scanner because of its privacy issues. Since its release in 2004,
it has been target several times because of its security measures. Over the course of time Facebook
did learn from its mistakes and improved its security measures of how people share information on
the platform. But an area where they still don’t have much control is the applications that are built
using the platform. Here is a statement from Facebook’s privacy policy about Third party
applications - we do not own or operate the applications or websites that use Facebook
Platform. That means that when you use those applications and websites you are making
your Facebook information available to someone other than Facebook.
This is where the users should be careful. Applications running on Facebook cannot be trusted unles
it belongs to a popular app builder. There are various such malicious and vulnerable Facebook
applications running on the platform which can misuse the information that you share. Facebook ha
become the prime target of spammers and hackers because of its heavy popularity among people
and because most of the users are unaware of such issues, they keep on clicking every application
that comes in their notification. The main aim of this paper is to make users aware of the fact that
every application on Facebook cannot be trusted.
While performing some tests on Facebook platform, I came across a vulnerable application that can
be attacked using Cross site scripting. The application can be found at this link :
http://apps.facebook.com/name_meaning/ . This application tells you the meaning of your name.


As you can see that the application has a text box where the user can enter his/her name to find out
the meaning. I went on to check this application with a normal reflected XSS attack by entering a
small javascript : <script>alert(“HackingAlert”)</script>
This injection didn’t work. So I went on to try my second dork with a bit of advanced script injection
to bypass the filter mechanism. The next javascript that I tried was :
>”><script>alert(“HackingAlert”)</script>” .
This time the attack succeeded and an alert message was generated showing the successful
execution of the script. 


I further went on to check if I can insert more dangerous tags or not. The next script that i crafted
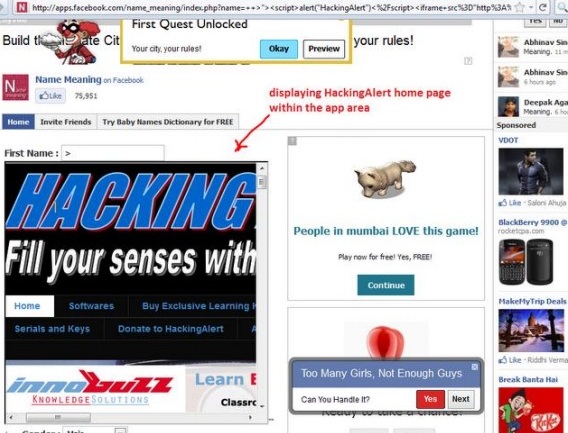
contained an <iframe> tag to check if my respective iframe gets displayed in place of the application
or not. The attack succeeded again and instead of displaying the application in the iframe area, it
displayed my blog url which I had inserted in my script.
Here is my crafted script :
>"><script>alert("HackingAlert")</script><iframe
src="http://hackingalert.blogspot.com" width="400" height="400"></iframe>"

NOTE – You will have to shift to http version of Facebook instead of https in order
to use any of its third party applications. 


 Now any attacker can display a malicious link in the iframe area and spread the url. The attacker can
use this technique to steal cookies and perform session hijacking.


Looking at this url, any normal user would believe that it belongs to the Facebook application. In-fact
it does belong to it but it has been crafted to attack the user information. This vulnerability can
easily be used to steal cookies of legitimate users and lead to their security breach.
Hence it is highly recommended that you should not trust any facebook application blindly. Recently
lots of spam and such vulnerable apps have flooded the platform and Facebook will not take any
responsibility for any information that you share with third party applications within the platform. So
think before you CLICK!!


Tuesday, August 23, 2011

read it...


The only way to prevent other social services from doing what Facebook does, we must only use federated (decentralized, with no private authority) free networks services (which run free software, aka open source software). 


Federated free networks services: 
StatusNet - http://status.net/

"We need to think deeply, and rapidly, and to good technological effect, about the consequences of what we have built and what we haven’t built yet. . . . [T]he over-centralization of network services is a crucial political vulnerability. Friends of ours, people seeking freedom, are going to get arrested, beaten, tortured, and eventually killed somewhere on earth because they’re depending for their political survival in their movements for freedom on technology we know is built to sell them out."

--Eben Moglen

"As the need for free (as in freedom) tools to communicate and socialize becomes increasingly urgent, more projects have been popping up to take up the challenge: GNU social and StatusNet, Crabgrass, Apache Wave, and more. The list goes on, and on. If you're not yet familiar with the issue, or even if you are, you should watch this excellent talk by Eben Moglen here: http://www.youtube.com/watch?v=gORNmfpD0ak

The first step towards digital autonomy is of course to stop using services that restrict your freedom, whether they do so through unfair terms of service, disregard for your privacy, locking you in, and/or any other means. Facebook is the biggest and baddest right now, so it's a great place to start. If you're like most Facebook users, you're probably thinking something along the lines of "This is great, but I could never afford to delete my Facebook account". Really though, it isn't that bad. Instead of just having one central web service you rely on, you'll just be spread out on what you're already using (phone, text, IM, email), and perhaps picking up some new tools. It is a small sacrifice, but the longterm payoff is great. Sometimes, what's slightly more convenient to you as an individual in the short term, is extremely harmful to society on a large scale."

Facebook is implementing face recognition by that everyone can identify anyone by a simplpicture of you tagged or posted under your real name. For example this could be implemented into the "INDECT" project http://en.wikipedia.org/wiki/INDECT and by that every camera with that technology (ready 2014) could recognize your face and identify you everywhere.


/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/\/

All steps explained on this OP: http://nd.gd/ub
 
AT  THIS STAGE, IT IS PRIMARILY AN AWARENESS CAMPAIGN! We are NOT taking FB  offline, for practical purposes. NO DDoS

There has been a gross misunderstanding, caused by the popularized video concerning #OperationFacebook. The video was made by a  non-native speaker of English. The word "kill" was used so various media outlets reported a plan of direct hacking attack on the infrastructure of Facebook. This inte
On July 16, 2011, someone created accounts for an “Operation Facebook” on YouTube (FacebookOp) and Twitter (OP_Facebook).  These account names are a little odd: why not just use one of the many  other mediums that Anonymous has used in the past? Fumore, the  released video, embedded above, is not of the usual computerized voice  and visual production quality that we’re used to from Anonymous.
The dates are also questionable: why didn’t 
rpretation is distracting from the context of the rest of the message, which aims to  warn citizens in a concentrated and creative way of the privacy and security risks involved in using Facebook.
 
GOALS:
  • Promote free software (aka open source) and federated (decentralized) alternatives like Status.net, Crabgrass, Apache Wave, and Diaspora. 
  • Expose Facebook's crimes to as many people as possible.
  • Scorn Facebook as much as possible in as many ways as we can scheme up.
  • Crea,hne multilingual propaganda, so the public and facebook know WHY
  • Discuss legal action in the chan. If you want to be a little punk troublemaker, then please keep it to PMs.
 
Methods:
  • Spread the information from this pad  //and this pad within anonymous
  • Spread home-made posters around your city
  • Get media attention and use it right to spread information.
  • Boycott and support alternatives
  • Botnets.
  • Mass fake profiles. 
  • Memes that mock Facebook. 
  • Hack admin/facebook related people
  • Social engineering for lulz and profit. (helps how?)
 
        POSTERS AND PROPAGANDA 
        
* Anti-FB logo: http://bit.ly/pHgY12
* Anti-FB posters: http://www.mediafire.com/?1y9whcfpu0ddtvx  (many languages) 
To Do: Upload the posters to a http://imgur.com/ album
* Concept-only for your own text: http://i.imgur.com/qP2GT.png

        LINKS

Also read:
 
· DNS Poisoning:
 
· Privacy Policy: #lang:es_PE 
*notice that you only agree to have your data shared with the apps you approve, or if there is a legal requirement (court order, etc.), they say NOTHING of selling your information, but do it anyway.
 
·August 1, 2011   Botnet could steal data via Facebook photos :

·Companies selling your information:
 
·Cracking/hacking tuts (only for the already mildly knowledgeable):
 
·OS ready to hack/crack,,,
 
·Facebook has been hacked before, several years ago:
http://foro.elhacker.netNormally, a networked computer uses a D #lang:es_ES  #lang:es_CL  #lang:es_PE NS server provided by the computer user's organization or an Internet service provider (ISP). DNS servers are generally deployed in an organization's network to improve resolution response performance by caching previously obtained query results. Poisoning attacks on a single DNS server can affect the users serviced directly by the compromised server or indirectly by its downstream server(s) if applicable.
To perform a cache poisoning attack, the attacker exploits a flaw in the DNS software. If the server does not correctly validate DNS responses to ensure that they are from an authoritative source (for example by using DNSSEC) the server will end up caching the incorrect entries locally and serve them to other users that make the same request.
This technique can be used to direct users of a website to another site of the attacker's choosing. For example, an attacker spoofs the IP address DNS entries for a target website on a given DNS server, replacing them with the IP address of a server he controls. He then creates files on the server he controls with names matching those on the target server. These files could contain malicious content, such as a computer worm or a computer virus. A user whose computer has referenced the poisoned DNS server would be tricked into accepting content coming from a non-authentic server and unknowingly download malicious content./hacking_basico/facebooks_servers_was_hacked_by_inj3ct0r_team_hack_of_the_year-t298374.0.html 
 Umm.. this isn't hacking facebook, this is spoofing a company's DNS.. big difference.
 
·Proof that FB actually IS selling our info to the government:
 
  
  THE MOST IMPORTANT THING WE NEED TO DO NOW IS MAKING A NEW VIDEO
It has to be english and a videoresponse to the 3million-views-video. It also has to include that everyone who is offended(whatever) by facebook can join us and that we don't just dos name some methods what we could do too. (also use the same tags as the first video)
Please make a nice text with those points here: http://www.anonpad.org/osmLaf3Pgt and someone with nice videoskills make the video. Get this started...

Facebook Applications Used For Phishing

It would be easy to think that once someone has logged in successfully to Facebook—and not a phishing site—that the security threat is largely gone. However, that’s not quite the case, as we’ve seen before.

Earlier this week, however, Trend Micro researcher Rik Ferguson found at least two—if not more—malicious applications on Facebook. (These were the Posts and Stream applications.) They were used for a phishing attack that sent users to a known phishing domain, with a page claiming that users need to enter their login credentials to use the application. The messages appear as notifications in a target user’s legitimate Facebook profile, as shown below. The links to the malicious site are highlighted:


After entering the credentials, users would then be redirected to Facebook itself. (The posts detailing these findings can be found at the Counter Measures blog; the initial report is here and a follow-up was posted here.)

While Trend Micro has informed Facebook of these findings, users should still exercise caution when entering login credentials. They should be doubly sure that these are being entered into legitimate sites, and not carefully crafted phishing sites. The particular site involved in this phishing attack is already blocked by the Smart Protection Network.

Monday, August 15, 2011

small tricks of Hacking.... For the Beginner.....

inurl:"ViewerFrame?Mode="
intitle:axis intitle:"video server"
inurl:indexFrame.shtml Axis
?intitle:index.of? mp3 artist-name-here
"intitle:index of"
"A syntax error has occurred" filetype:ihtml
"access denied for user" "using password"
"Chatologica MetaSearch" "stack tracking:"
"Index of /backup"
"ORA-00921: unexpected end of SQL command"
"parent directory " /appz/ -xxx -html -htm -php -shtml -opendivx -md5 -md5sums
"parent directory " DVDRip -xxx -html -htm -php -shtml -opendivx -md5 -md5sums
"parent directory " Gamez -xxx -html -htm -php -shtml -opendivx -md5 -md5sums
"parent directory " MP3 -xxx -html -htm -php -shtml -opendivx -md5 -md5sums
"parent directory " Name of Singer or album -xxx -html -htm -php -shtml -opendivx -md5 -md5sums
"parent directory "Xvid -xxx -html -htm -php -shtml -opendivx -md5 -md5sums
?intitle:index.of? mp3 name
allintitle:"Network Camera NetworkCamera"
allinurl: admin mdb
allinurl:auth_user_file.txt
intitle:"live view" intitle:axis
intitle:axis intitle:"video server"
intitle:liveapplet
inurl:"ViewerFrame?Mode="
inurl:axis-cgi/jpg
inurl:axis-cgi/mjpg (motion-JPEG)
inurl:passlist.txt
inurl:view/index.shtml
inurl:view/indexFrame.shtml
inurl:view/view.shtml
inurl:ViewerFrame?Mode=Refresh
liveapplet
!Host=*.* intext:enc_UserPassword=* ext:pcf
" -FrontPage-" ext:pwd inurl:(service | authors | administrators | users)
"A syntax error has occurred" filetype:ihtml
"About Mac OS Personal Web Sharing"
"access denied for user" "using password"
"allow_call_time_pass_reference" "PATH_INFO"
"An illegal character has been found in the statement" -"previous message"
"ASP.NET_SessionId" "data source="
"AutoCreate=TRUE password=*"
"Can't connect to local" intitle:warning
"Certificate Practice Statement" inurl:(PDF | DOC)
"Chatologica MetaSearch" "stack tracking"
"Copyright © Tektronix, Inc." "printer status"
"detected an internal error [IBM][CLI Driver][DB2/6000]"
"Dumping data for table"
"Error Diagnostic Information" intitle:"Error Occurred While"
"error found handling the request" cocoon filetype:xml
"Fatal error: Call to undefined function" -reply -the -next
"Generated by phpSystem"
"generated by wwwstat"
"Host Vulnerability Summary Report"
"HTTP_FROM=googlebot" googlebot.com "Server_Software="
"IMail Server Web Messaging" intitle:login
"Incorrect syntax near"
"Index of /" +.htaccess
"Index of /" +passwd
"Index of /" +password.txt
"Index of /admin"
"Index of /mail"
"Index Of /network" "last modified"
"Index of /password"
"index of /private" site:mil
"index of /private" -site:net -site:com -site:org
"Index of" / "chat/logs"
"index of/" "ws_ftp.ini" "parent directory"
"Installed Objects Scanner" inurl:default.asp
"Internal Server Error" "server at"
"liveice configuration file" ext:cfg
"Login - Sun Cobalt RaQ"
"Mecury Version" "Infastructure Group"
"Microsoft ® Windows * ™ Version * DrWtsn32 Copyright ©" ext:log
"More Info about MetaCart Free"
"Most Submitted Forms and Scripts" "this section"
"mysql dump" filetype:sql
"mySQL error with query"
"Network Vulnerability Assessment Report"
"not for distribution" confidential
"ORA-00921: unexpected end of SQL command"
"ORA-00933: SQL command not properly ended"
"ORA-00936: missing expression"
"pcANYWHERE EXPRESS Java Client"
"phone * * *" "address *" "e-mail" intitle:"curriculum vitae"
"phpMyAdmin MySQL-Dump" "INSERT INTO" -"the"
"phpMyAdmin MySQL-Dump" filetype:txt
"phpMyAdmin" "running on" inurl:"main.php"
"PostgreSQL query failed: ERROR: parser: parse error"
"Powered by mnoGoSearch - free web search engine software"
"powered by openbsd" +"powered by apache"
"Powered by UebiMiau" -site:sourceforge.net
"produced by getstats"
"Request Details" "Control Tree" "Server Variables"
"robots.txt" "Disallow:" filetype:txt
"Running in Child mode"
"sets mode: +k"
"sets mode: +p"
"sets mode: +s"
"Supplied argument is not a valid MySQL result resource"
"Supplied argument is not a valid PostgreSQL result"
"Thank you for your order" +receipt
"This is a Shareaza Node"
"This report was generated by WebLog"
"This summary was generated by wwwstat"
"VNC Desktop" inurl:5800
"Warning: Cannot modify header information - headers already sent"
"Web File Browser" "Use regular expression"
"xampp/phpinfo
"You have an error in your SQL syntax near"
"Your password is * Remember this for later use"
aboutprinter.shtml
allintitle: "index of/admin"
allintitle: "index of/root"
allintitle: restricted filetype :mail
allintitle: restricted filetype:doc site:gov
allintitle: sensitive filetype:doc
allintitle:.."Test page for Apache Installation.."
allintitle:admin.php
allinurl:".r{}_vti_cnf/"
allinurl:admin mdb
allinurl:auth_user_file.txt
allinurl:servlet/SnoopServlet
An unexpected token "END-OF-STATEMENT" was found
camera linksys inurl:main.cgi
Canon Webview netcams
Comersus.mdb database
confidential site:mil
ConnectionTest.java filetype:html
data filetype:mdb -site:gov -site:mil
eggdrop filetype:user user
ext:conf NoCatAuth -cvs
ext:pwd inurl:(service | authors | administrators | users) "# -FrontPage-"
ext:txt inurl:unattend.txt
filetype:ASP ASP
filetype:ASPX ASPX
filetype:BML BML
filetype:cfg ks intext:rootpw -sample -test -howto
filetype:cfm "cfapplication name" password
filetype:CFM CFM
filetype:CGI CGI
filetype:conf inurl:psybnc.conf "USER.PASS="
filetype:dat "password.dat
filetype:DIFF DIFF
filetype:DLL DLL
filetype:DOC DOC
filetype:FCGI FCGI
filetype:HTM HTM
filetype:HTML HTML
filetype:inf sysprep
filetype:JHTML JHTML
filetype:JSP JSP
filetype:log inurl:password.log
filetype:MV MV
filetype:pdf "Assessment Report" nessus
filetype:PDF PDF
filetype:PHP PHP
filetype:PHP3 PHP3
filetype:PHP4 PHP4
filetype:PHTML PHTML
filetype:PL PL
filetype:PPT PPT
filetype:PS PS
filetype:SHTML SHTML
filetype:STM STM
filetype:SWF SWF
filetype:TXT TXT
filetype:XLS XLS
htpasswd / htpasswd.bak
Index of phpMyAdmin
index of: intext:Gallery in Configuration mode
index.of passlist
intext:""BiTBOARD v2.0" BiTSHiFTERS Bulletin Board"
intext:"d.aspx?id" || inurl:"d.aspx?id"
intext:"enable secret 5 $"
intext:"powered by Web Wiz Journal"
intext:"SteamUserPassphrase=" intext:"SteamAppUser=" -"username" -"user"
intitle:"--- VIDEO WEB SERVER ---" intext:"Video Web Server" "Any time & Any where" username password
intitle:"500 Internal Server Error" "server at"
intitle:"actiontec" main setup status "Copyright 2001 Actiontec Electronics Inc"
intitle:"Browser Launch Page"
intitle:"DocuShare" inurl:"docushare/dsweb/" -faq -gov -edu
intitle:"EverFocus.EDSR.applet"
intitle:"Index of" ".htpasswd" "htgroup" -intitle:"dist" -apache -htpasswd.c
intitle:"Index of" .bash_history
intitle:"Index of" .mysql_history
intitle:"Index of" .sh_history
intitle:"Index of" cfide
intitle:"index of" etc/shadow
intitle:"index of" htpasswd
intitle:"index of" intext:globals.inc
intitle:"index of" master.passwd
intitle:"index of" members OR accounts
intitle:"index of" passwd
intitle:"Index of" passwords modified
intitle:"index of" people.lst
intitle:"index of" pwd.db
intitle:"Index of" pwd.db
intitle:"index of" spwd
intitle:"Index of" spwd.db passwd -pam.conf
intitle:"index of" user_carts OR user_cart
intitle:"Index of..etc" passwd
intitle:"iVISTA.Main.Page"
intitle:"network administration" inurl:"nic"
intitle:"OfficeConnect Cable/DSL Gateway" intext:"Checking your browser"
intitle:"remote assessment" OpenAanval Console
intitle:"Remote Desktop Web Connection" inurl:tsweb
intitle:"switch login" "IBM Fast Ethernet Desktop"
intitle:"SWW link" "Please wait....."
intitle:"teamspeak server-administration
intitle:"TUTOS Login"
intitle:"VMware Management Interface:" inurl:"vmware/en/"
intitle:"Welcome to the Advanced Extranet Server, ADVX!"
intitle:"Welcome to Windows 2000 Internet Services"
intitle:"Connection Status" intext:"Current login"
intitle:"inc. vpn 3000 concentrator"
intitle:asterisk.management.portal web-access
intitle:dupics inurl:(add.asp | default.asp | view.asp | voting.asp) -site:duware.com
intitle:index.of administrators.pwd
intitle:index.of cgiirc.config
intitle:Index.of etc shadow site:passwd
intitle:index.of intext:"secring.skr"|"secring.pgp"|"secring.bak"
intitle:index.of master.passwd
intitle:index.of passwd passwd.bak
intitle:index.of people.lst
intitle:index.of trillian.ini
intitle:Novell intitle:WebAccess "Copyright *-* Novell, Inc"
intitle:opengroupware.org "resistance is obsolete" "Report Bugs" "Username" "password"
intitle:open-xchange inurl:login.pl
inurl:":10000" intext:webmin
inurl:"8003/Display?what="
inurl:"auth_user_file.txt"
inurl:"GRC.DAT" intext:"password"
inurl:"printer/main.html" intext:"settings"
inurl:"slapd.conf" intext:"credentials" -manpage -"Manual Page" -man: -sample
inurl:"slapd.conf" intext:"rootpw" -manpage -"Manual Page" -man: -sample
inurl:"ViewerFrame?Mode="
inurl:"wvdial.conf" intext:"password"
inurl:"wwwroot/
inurl:/Citrix/Nfuse17/
inurl:/db/main.mdb
inurl:/wwwboard
inurl:access
inurl:admin filetype:db
inurl:asp
inurl:buy
inurl:ccbill filetype:log
inurl:cgi
inurl:cgiirc.config
inurl:config.php dbuname dbpass
inurl:data
inurl:default.asp intitle:"WebCommander"
inurl:download
inurl:file
inurl:filezilla.xml -cvs
inurl:forum
inurl:home
inurl:hp/device/this.LCDispatcher
inurl:html
inurl:iisadmin
inurl:inc
inurl:info
inurl:lilo.conf filetype:conf password -tatercounter2000 -bootpwd -man
inurl:list
inurl:login filetype:swf swf
inurl:mail
inurl:midicart.mdb
inurl:names.nsf?opendatabase
inurl:new
inurl:nuke filetype:sql
inurl:order
inurl:ospfd.conf intext:password -sample -test -tutorial -download
inurl:pages
inurl:pap-secrets -cvs
inurl:passlist.txt
Ultima Online loginservers
inurl:Proxy.txt
inurl:public
inurl:search
inurl:secring ext:skr | ext:pgp | ext:bak
inurl:shop
inurl:shopdbtest.asp
inurl:software
inurl:support
inurl:user
inurl:vtund.conf intext:pass -cvs s
inurl:web
inurl:zebra.conf intext:password -sample -test -tutorial -download
LeapFTP intitle:"index.of./" sites.ini modified
POWERED BY HIT JAMMER 1.0!
signin filetype:url
site:ups.com intitle:"Ups Package tracking" intext:"1Z ### ### ## #### ### #"
top secret site:mil
Ultima Online loginservers
VP-ASP Shop Administrators only
XAMPP "inurl:xampp/index"

filetype:asp ?Custom Error Message? Category Source

filetype:asp +?[ODBC SQL]?

filetype:log ?PHP Parse error? |?PHP Warning?|?PHP error?

filetype:php inurl:?logging.php? ?Discuz? error

ht://Dig htsearch error

ISS 4.0 error messages

ISS web server error messages

internal server error

intext:?Error Message : Error loading required libraries.?

intext:?Warning: Failed opening? ?on line? ?include_path?

intitle:?Apache Tomcat? ?Error Report?

intitle:?Default PLESK Page?

intitle:?Execution of this script not permitted?

intitle:?Under construction? ?does not currently have?
intitle:phpMyAdmin "welcome to phpMyAdmin*** "runing on*as root@*"
inurl:com_xmovie

Related Posts Plugin for WordPress, Blogger...